Your number and your accounts need separate recovery
If your phone unexpectedly loses cellular service and you receive an alert about a SIM replacement you did not request, contact your carrier through an independently verified channel immediately. While it investigates, use a trusted internet connection to protect accounts that depend on that number. Restoring reception is only one part of recovery.
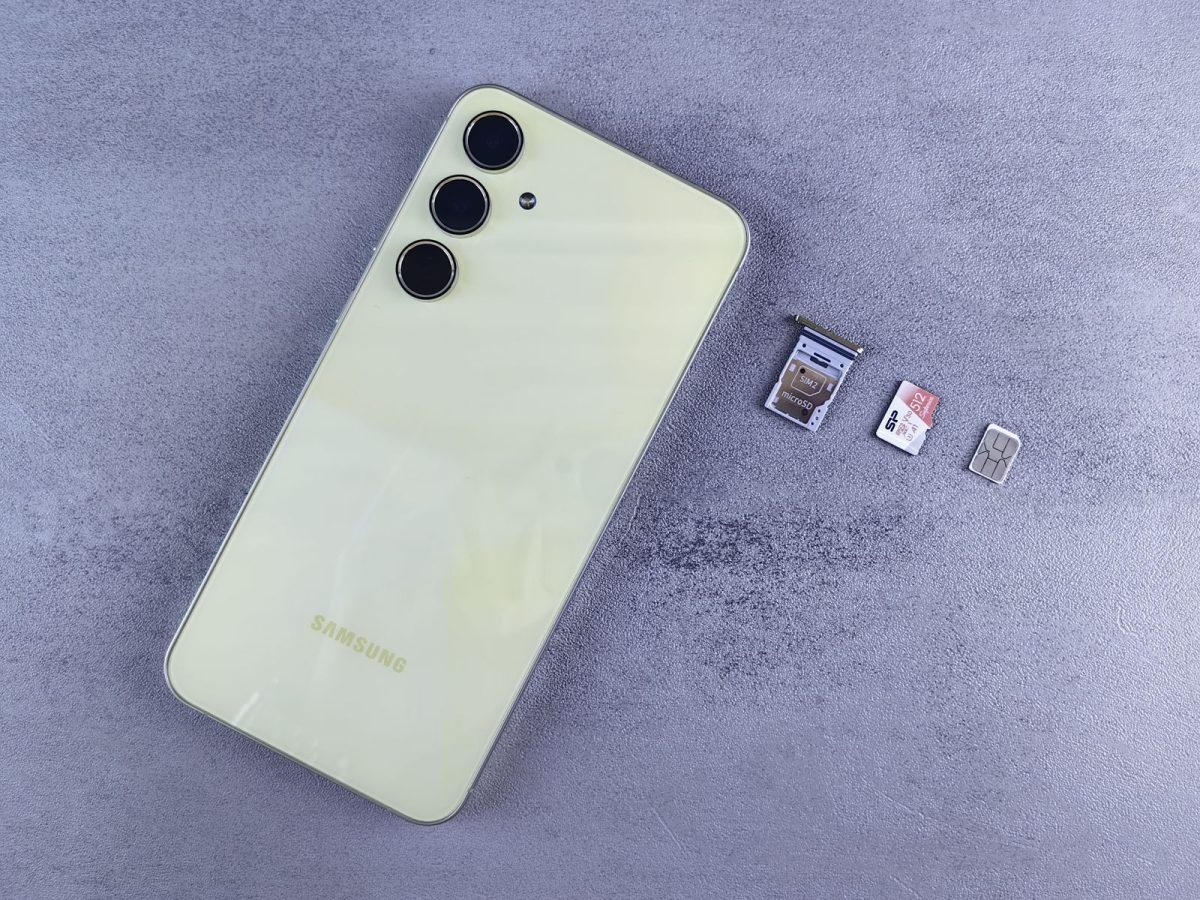
A fraudulent SIM swap moves your number to another SIM or eSIM. Someone holding your number may receive verification messages intended for you. That does not establish that every account has been opened, but it makes phone-based recovery a weak link. An eSIM does not remove this risk, as the Canadian Centre for Cyber Security explains.
The practical aim is to answer two questions independently: who currently controls delivery to your number, and who can still access or reset your important accounts? Keep separate notes for each. A carrier case marked resolved cannot answer the second question.
Separate a warning pattern from a reception problem
Sudden service loss can also come from coverage, an outage, billing or a legitimate activation. Missing one text is not proof of a takeover. Look for a combination: an unrequested SIM or transfer notice, changed carrier-account details, unexpected password-reset messages, or loss of access to an online account. Working chat over Wi-Fi does not prove your cellular number is safe.
Hypothetically, Maya is at home when cellular calls stop. Her laptop still has internet, and an email says her mobile account contact address changed. She did not request a change. She should report both facts together rather than spend the afternoon resetting network settings. If instead she arranged a replacement SIM that morning, the same service loss has a different explanation to check.
Record when you noticed the failure and preserve alerts with their timestamps. Do not follow their links to investigate. Open the carrier's known website yourself or use contact details from an existing bill. Avoid erasing the phone or deleting its eSIM during the investigation; preserve the current state until the carrier explains its recovery procedure.
Give the carrier a specific fraud report
The FTC recommends immediate contact with your cellular provider. Use another phone, an official online support route over Wi-Fi, or a carrier store if you cannot call. For an employer-owned line, involve the organisation's telecom administrator too.
Say: “I suspect an unauthorised SIM replacement or number transfer. I still have my phone. Service stopped at approximately this time, and I did not authorise this change.” Ask support to check:
- Whether a replacement SIM or eSIM was activated, or the number transferred elsewhere, and when.
- Whether account contact information or security credentials changed without permission.
- What it can do now to stop unauthorised changes and restore the number to your control.
Ask for the fraud case reference, an alternative contact route you control, and the next action expected from you. Provide identity evidence only through the verified process the carrier identifies. Never give a caller a code merely because they claim to be reversing the swap.
Checkpoint: write down whether the carrier confirmed a change, ruled one out, or is still investigating. “We will look into it” is a pending result. If normal support cannot investigate, ask for its fraud escalation route. Do not assume a universal reversal time or cancel the number as a shortcut.
Protect the accounts that can unlock others
While the carrier works, make a short account list on a trusted device. Start with your main email, password manager, financial services and any account showing suspicious activity. Move an account with active financial loss to the front. For a work account, notify your IT team through a known channel.
For each entry, note three things: whether you are still signed in, whether you have an enrolled method independent of this number, and whether anything changed unexpectedly. Do not request repeated text codes while delivery is in doubt. Try an already enrolled authenticator, security key or stored recovery code where the provider offers it. If none works, use that provider's official recovery process; a carrier cannot restore an unrelated email account.
Keep a surviving trusted session available while establishing another valid route. Do not sign out everywhere first and discover that the only way back sends a code to the disputed number. Once you can authenticate safely, change a compromised password, replace reused copies elsewhere, and inspect recovery details. Follow the provider's instructions for ending unfamiliar sessions.
Use a small record such as “email: access retained, recovery reviewed, unfamiliar session removed” or “bank: locked out, fraud case open”. This exposes unfinished work. A password changed successfully is useful evidence, but it does not establish that every recovery route and existing session is safe.
Check email for a route back in
Email deserves a separate inspection because it receives other services' reset links. For Google accounts, the compromised-account guide documents reviewing recent security events and devices, correcting unfamiliar recovery information, reviewing applications with access, and removing Gmail forwarding or filters you did not create. Use its account-recovery link if you cannot sign in.
In your Google Account, open Security & sign-in, then review the recent security events. Follow the documented response for activity that was not yours. Review devices too. Check recovery email, recovery phone and verification methods for changes, then inspect Gmail settings for forwarding, delegation and filters you did not authorise.
Checkpoint: reopen the relevant settings after saving corrections. Record any unfamiliar entry that remains or cannot be removed, and continue through official recovery help. For other email providers, use their own compromised-account instructions; menu names and session controls differ.
Hypothetically, a newly added forwarding destination remains after Maya changes her password. That is an unresolved access route, even though her new password works. Removing it addresses future forwarding; it cannot retrieve messages already copied.
Escalate losses without waiting for phone repair
Open financial services through their official apps or independently entered websites. Review recent transactions and account changes. Report anything unauthorised through the institution's verified fraud channel immediately, explaining that control of your number is disputed. Ask what restrictions and identity checks it can apply while delivery is unsafe. Do not assume changing your online password cancels a pending transfer.
Keep transaction references, alert times and case numbers together without storing passwords or recovery codes in the incident note. The FTC also directs US readers whose identity information may be exposed to IdentityTheft.gov. Outside the US, use your local official identity-theft reporting route. Available protections and recovery outcomes depend on the institution and jurisdiction.
Verify both recoveries before calling it finished
After the carrier says the number is restored, check an ordinary incoming call and an ordinary SMS from a trusted person. Specify SMS rather than an internet messaging service. Check outgoing calling too. If any direction fails, report that exact result against the carrier case. Reception bars alone are insufficient evidence that messages to your number arrive correctly.
Ask the carrier which additional account verification and SIM-change or port protection it offers, and what each control covers. Choose a unique carrier-account password and PIN where available. Follow its instructions rather than assuming a phone's local SIM PIN prevents provider-side account changes.
For sensitive online accounts, replace dependence on SMS where supported with an authenticator or security key, retaining a separate recovery method. Confirm the replacement works before removing an essential fallback. Revisit the account list: unresolved recovery details, suspicious sessions and disputed transactions each need their own follow-up. Successful delivery today does not undo access gained while someone else controlled the number.
Sources, versions & scope
The steps describe the documented controls and expected checks; they are not a claim that every device or software release has been physically tested. Platform and version differences are stated with the procedure.